Switch a device fingerprint in one tap — and see how far spoofing gets
Sandbox is a root-free Android device-fingerprint editor. No flashing, no bootloader unlock — set a complete device profile per app: model, screen, system and strong identifiers, all spoofed together.
Why a detection site publishes a spoofing tool
Because you cannot evaluate a detector without seeing what good spoofing looks like. This site sells fingerprint reference data and emulator negatives for spotting fakes, refurbs and cloud phones — and the only honest way to test those rules is to point a competent spoofer at them. Sandbox is that control sample: it rewrites 15 dimensions and keeps them internally consistent. If your risk engine stays quiet against it, your rules have a hole.
A whole-device profile, not just a model name
Many tools change only a few obvious fields — the model looks right but the fingerprint doesn't match, and cross-checks give it away. Sandbox covers 15 dimensions at once and keeps them consistent.
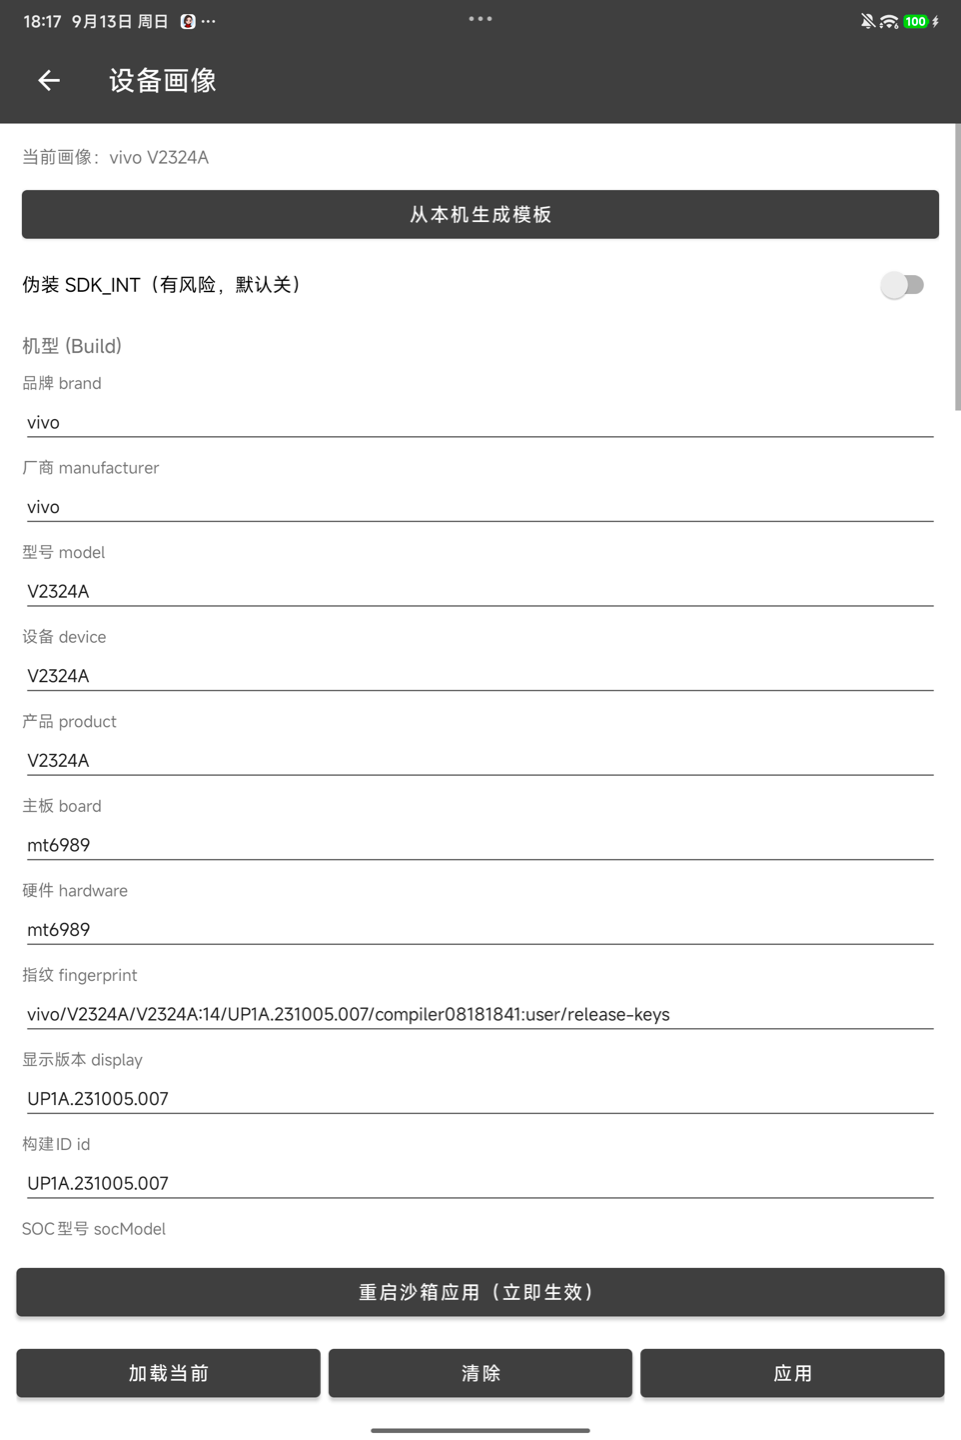
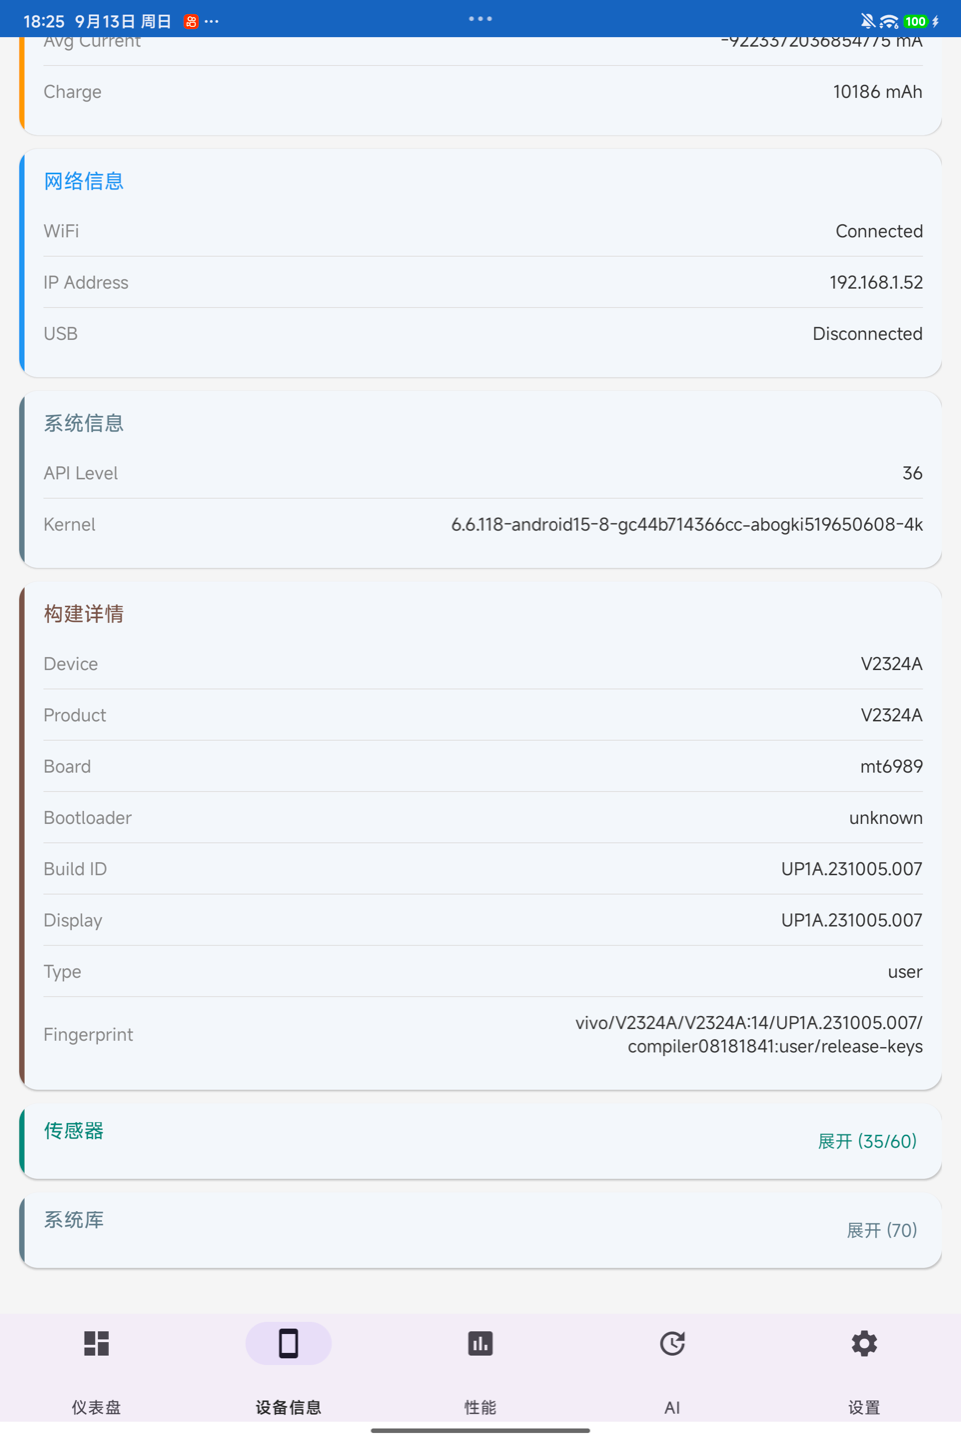
- Model: brand / manufacturer / model / fingerprint / board / SoC
- Sensors: the whole inventory — name, vendor and type, spoofed entry by entry. A real handset reports 30+; a mismatched count or part number is one of the easiest tells to catch
- Memory & storage: total RAM and storage capacity — a flagship model reporting 1 GB of RAM gives itself away instantly
- Screen: resolution / DPI
- System: Android version / SDK level
- Strong IDs: Android ID / Ad ID / DRM ID / serial / IMEI / IMSI
- SIM / carrier: operator / SIM state / SIM number / phone number
Three ways to build a profile
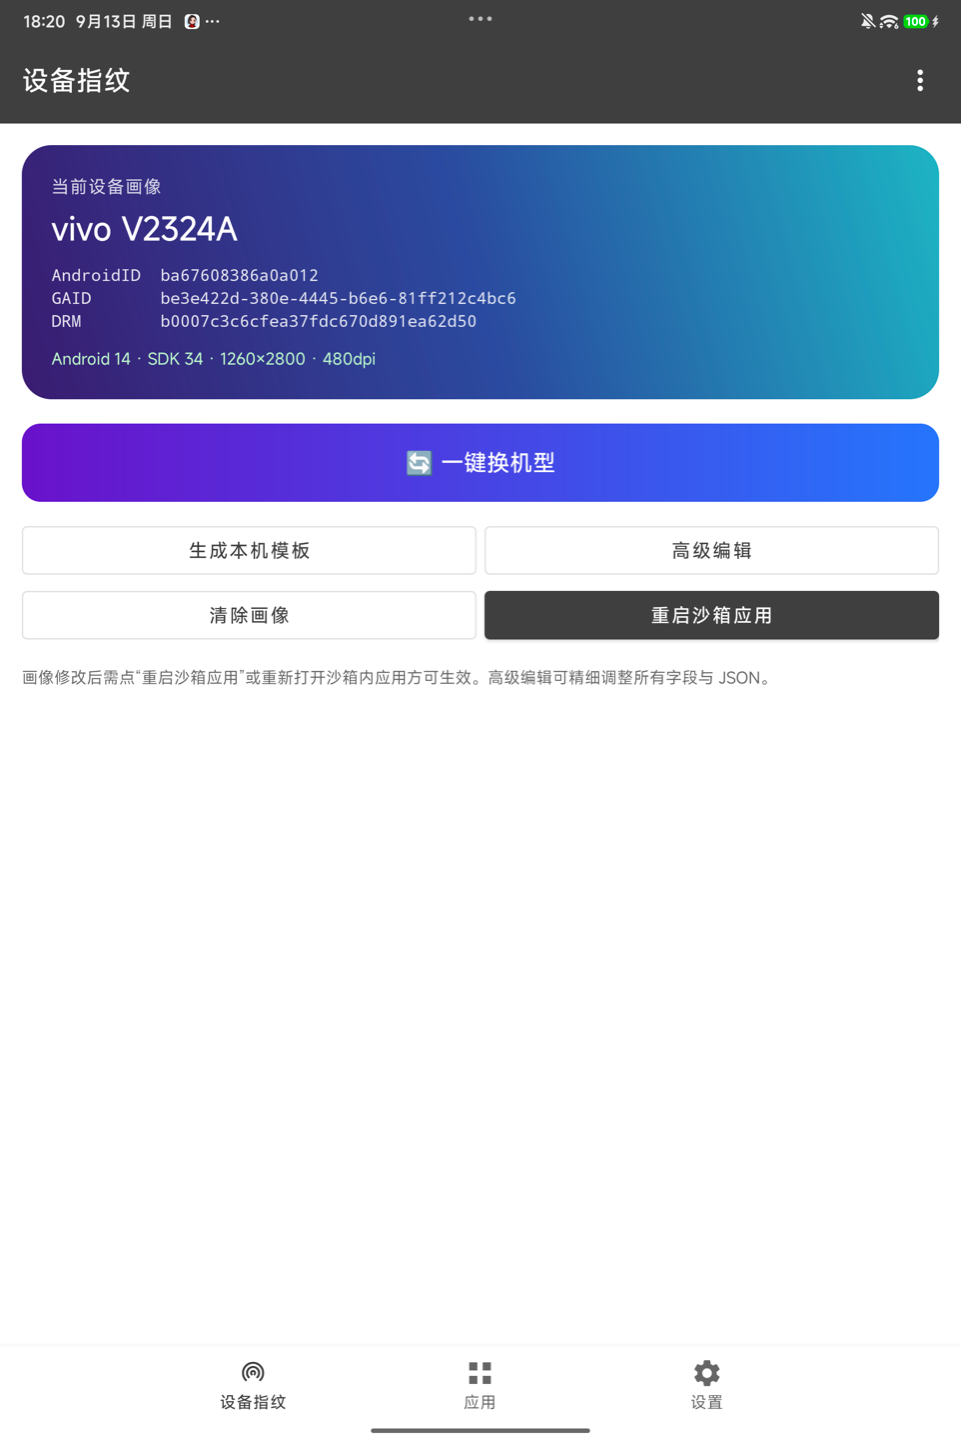
- One-tap model swap — a random real-device profile from a built-in library
- Clone this phone — start from your current device, then tweak
- Advanced edit — per-field control, or paste a full JSON fingerprint
The datasets on this site paste straight in
Sandbox ships an importer for this site's collection format — the complete JSON for all 119 handsets in the $19 dataset can be pasted in as a working profile, with no hand conversion.
See the $19 telemetry set → Derived identifiers that actually match
Missing fields in an imported profile get filled in with well-formed values that agree with each other — the exact step most similar tools get wrong, and the one detection teams should be checking.
- Carrier, IMSI, ICCID, IMEI and phone number are generated automatically
- IMSI prefix matches the carrier, ICCID prefix matches the carrier, IMEI passes its check digit
- The same profile yields the same values on every launch — no drift between runs
Verify the result on the spot
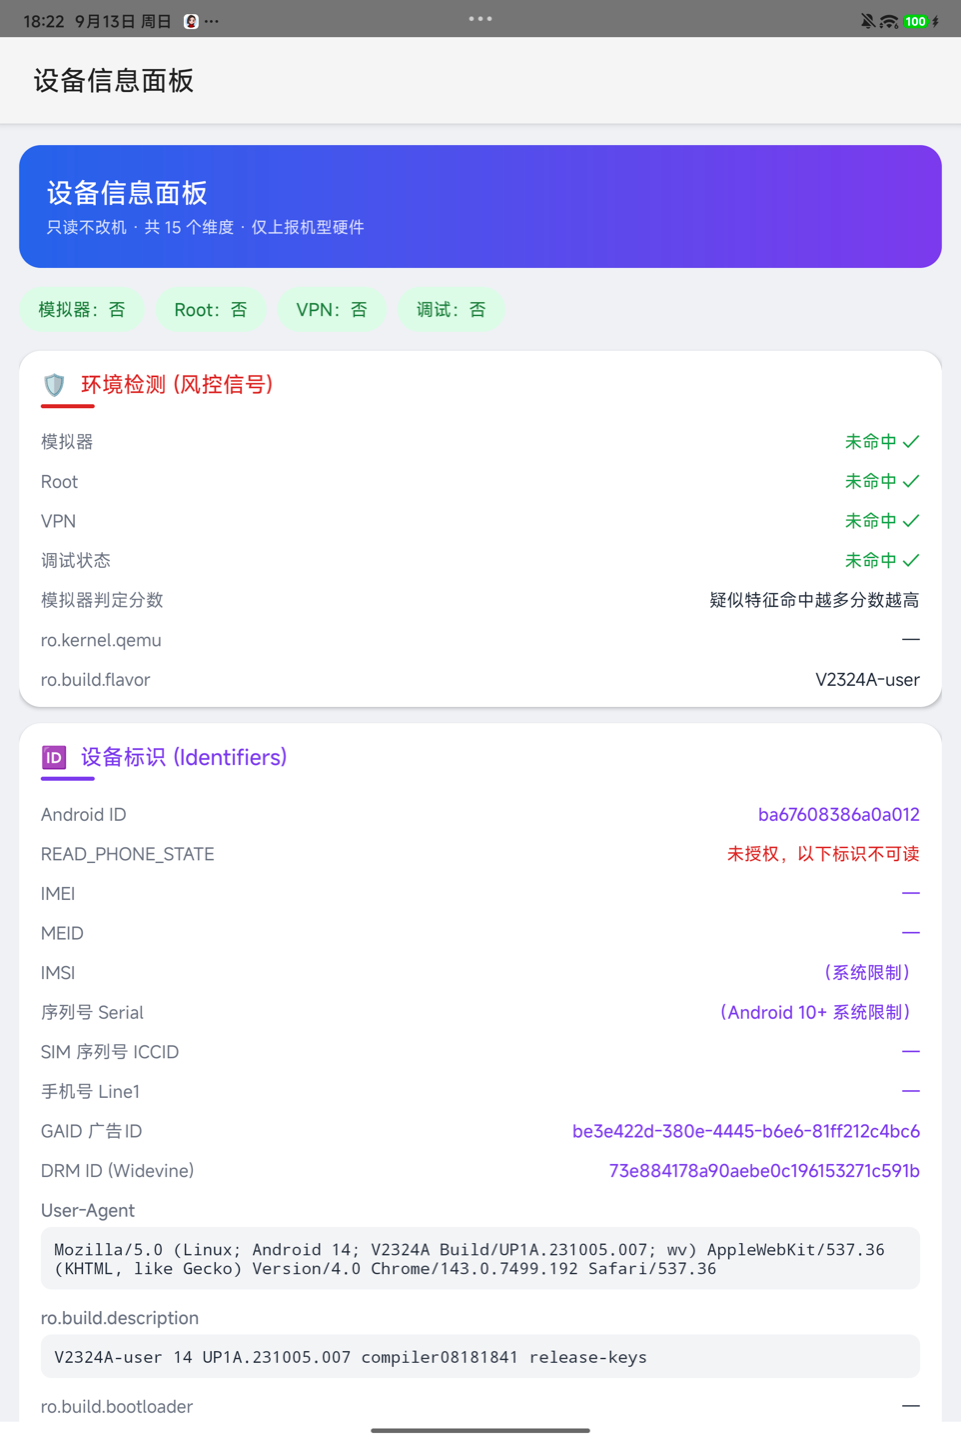
A built-in device-info panel shows the profile that is actually in effect, plus a self-check of risk signals: emulator / root / VPN / debug. Third-party detectors read the same target model.
Isolated apps, separate identities
Each managed app runs in its own space: data, accounts and fingerprints stay separate, and several apps can be managed side by side.
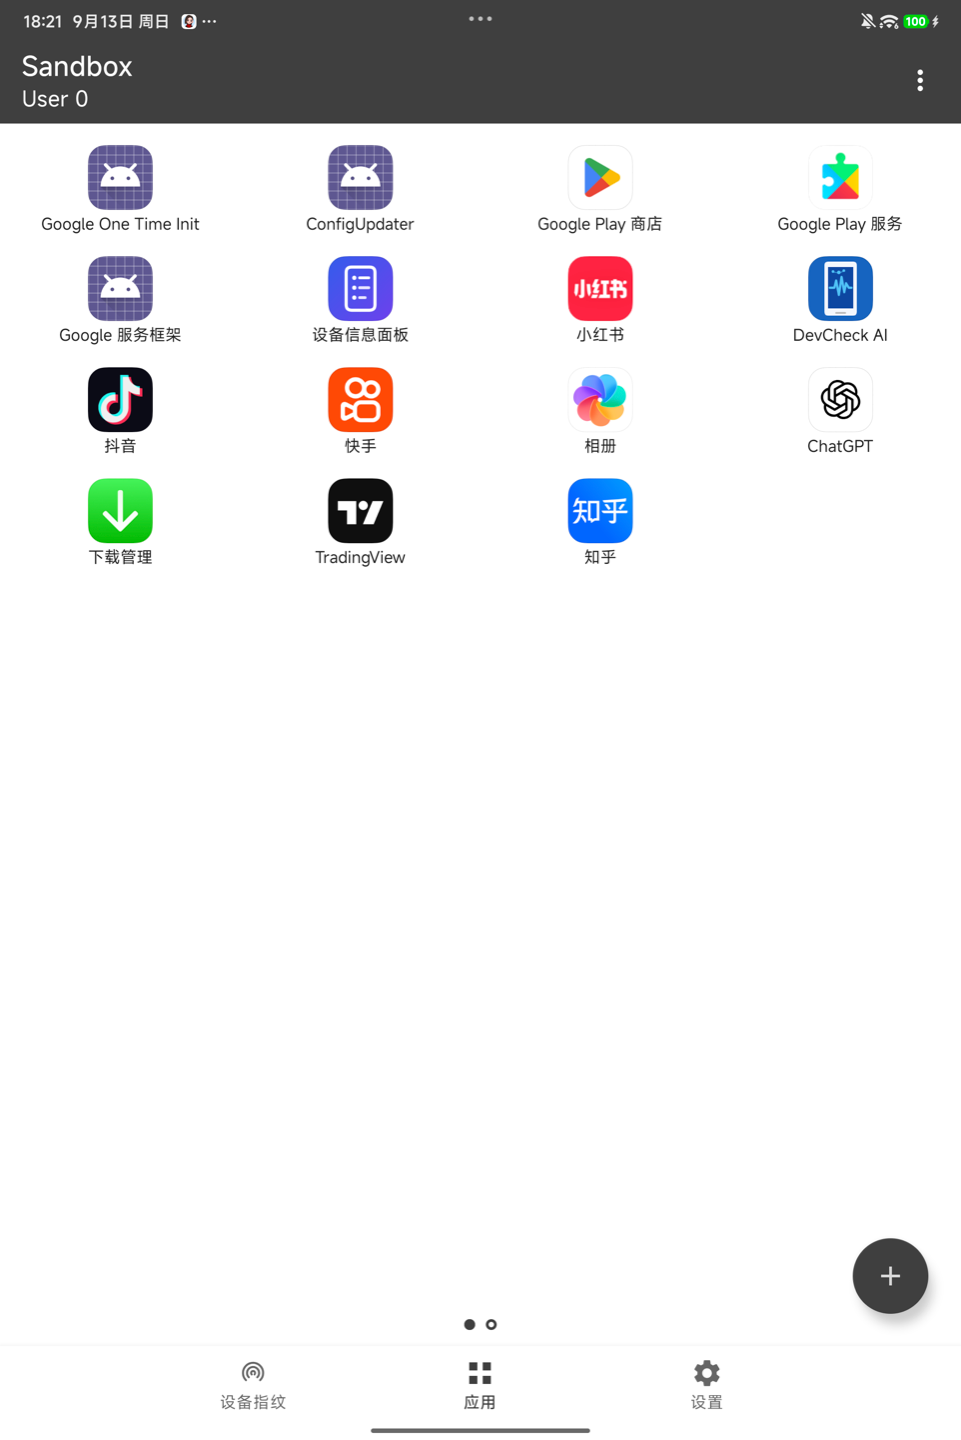
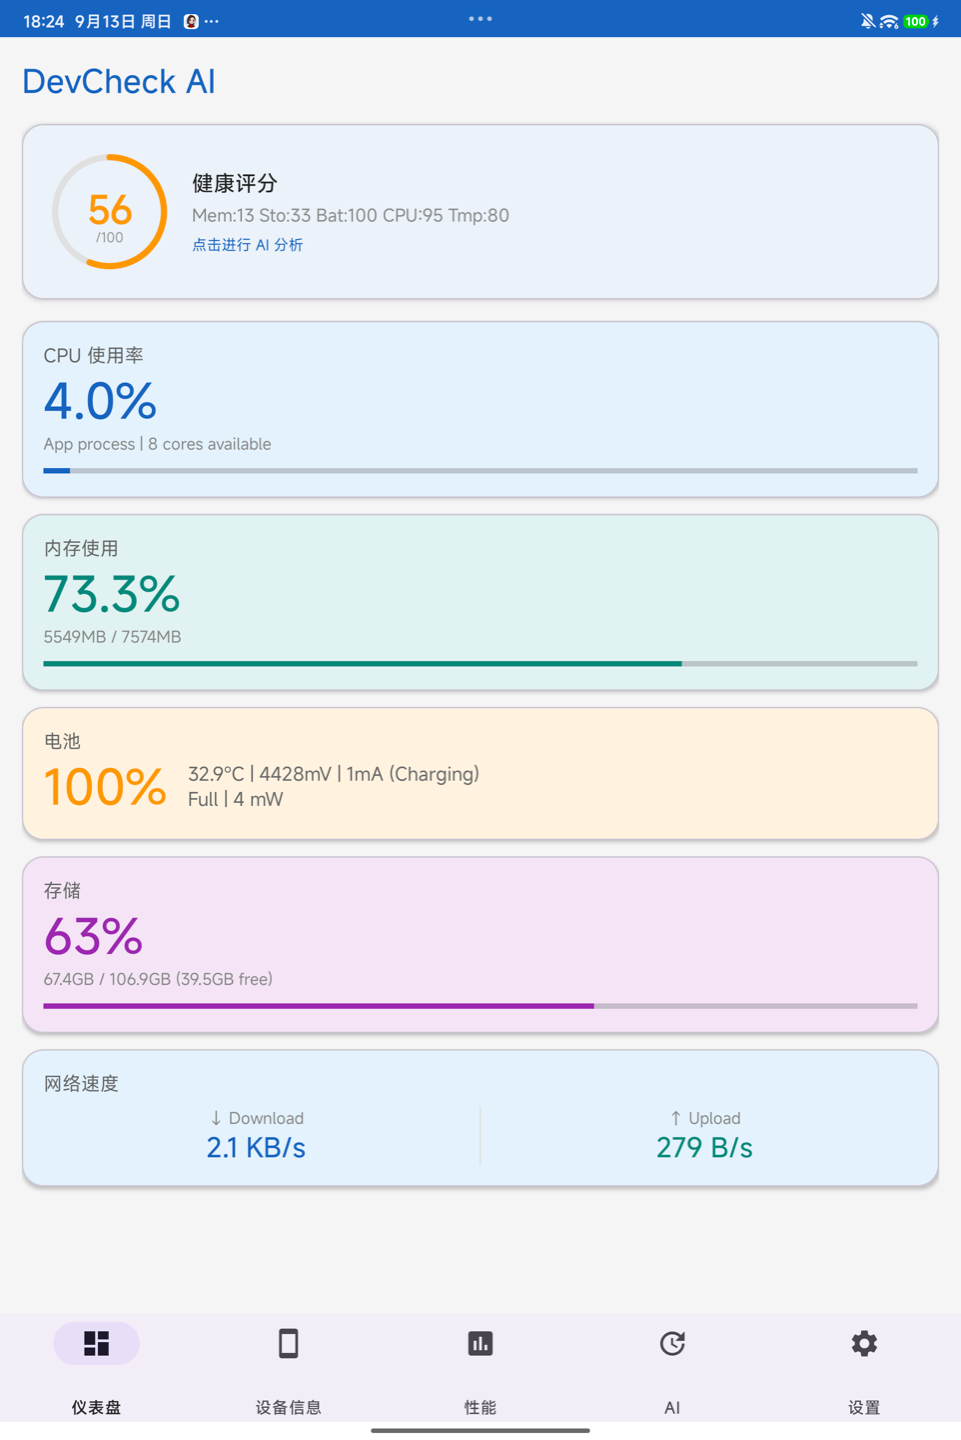
Measured with a third-party detector
Same handset, before and after: an independent detection tool reads two different devices.
Specs
- Requires
- Mainstream Android versions
- ABIs
- arm64-v8a / armeabi-v7a
- Size
- ~4.7 MB
- Root
- Not needed
FAQ
Does it need root?
No. No flashing, no bootloader unlock, no Xposed — install and run.
Does the profile persist?
Yes. Profiles are stored and survive reboots; the same profile produces the same values.
Can different apps get different fingerprints?
Yes. Every managed app has its own space and its own profile.
How do I confirm it worked?
The built-in panel shows the live profile, and any third-party detector will corroborate it.
Why does install warn about an unknown source or signature?
v4.0.0 ships with a debug signature, so Android flags it as an unknown source. Because the signing key differs, this build cannot upgrade over a same-named app from another channel.
The other side: data for detectors
If you came looking for detection baselines, the fingerprint datasets are what you want — including 12 emulator and 15 rooted records as negatives.
See the fingerprint datasets →Put a new device on your phone
Download APK · v4.0.0- Use it lawfully and with authorization, respecting the terms of service of any platform involved and the laws that apply where you are.
- It is intended for privacy protection and technical testing — validating anti-fraud rules against a known spoofer, app compatibility work, and keeping real hardware identifiers away from apps you don't trust.
- It is not for defeating platform risk controls to commit fraud, mass-register accounts, inflate metrics, or otherwise harm others. Consequences of misuse are the user's own.